Cryptographic Key Administration Lifecycle Pptx
The sensible aim is to keep keys bound to a clear owner, objective, cryptoperiod, and control airplane so the organisation can show the place every key’s, who can use it, and when it must be replaced. Managing every section is crucial as a end result of weak spot in a single stage undermines the entire lifecycle. For occasion, utilizing sturdy algorithms however storing keys in plain text on a file system negates the advantages of encryption. Similarly, failing to rotate keys after a system administrator leaves the company can expose delicate data. A thorough lifecycle ensures that keys remain confidential, integral and available—aligning with ISO 27001’s core principles.
How Lengthy Does Iso 27001 Certification Take?
- Automation can make all of the difference, streamlining the encryption key lifecycle from technology and storage to rotation and deletion.
- With Sectigo, strict protocols forestall unauthorized individuals from recovering non-public keys.
- Automation plays an more and more crucial function in key administration methods.
- Auditors evaluate documentation (cryptographic policy, lifecycle procedures), examine proof of key technology, storage, rotation and destruction, and interview workers.
- As digital gatekeepers, these keys hold info absolutely protected by controlling who can access it.
Cloud-native applications typically handle encryption internally using service-level encryption. With Out centralized oversight, this results in fragmented key visibility and governance, increasing the danger of mismanagement or key exposure. The rise of quantum computing represents some of the profound shifts in cybersecurity. Although fully capable quantum computers have not yet materialized, the “Harvest Now, Decrypt Later” menace mannequin is already energetic.
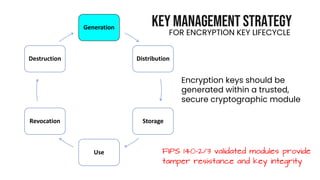
Encryption serves as a important line of defense, safeguarding information by rendering it unreadable without a decryption key. However, the security of encrypted knowledge hinges entirely on the correct administration of those keys. ISO Management A 8.24 requires organisations to outline and implement guidelines for cryptography and key management that defend confidentiality, integrity and authenticity of data. NIST reminds us that key management encompasses secure era, storage, distribution, utilization and destruction. With Out a structured lifecycle, encryption devolves into a false sense of security.
Post-quantum Cryptography Readiness

It provides intelligence to entry insurance policies by adapting them primarily based on utilization developments and risk intelligence. Cryptographic key management in 2025 and beyond is characterised by coping with evolving threats, tightening regulations, and rapidly advancing applied sciences. Organizations are not simply securing information; they’re navigating an increasingly complicated internet of digital identities and operational resilience calls for.
Why Key Management Breaks Down At Scale
Many laws (HIPAA, GDPR, SOC 2) anticipate https://codewithcoffee.com/intern-software-testing-humans/ encryption, making it a common control throughout frameworks. Hardware security modules (HSMs) promote the safe management and storage of cryptographic keys. These can take many forms and may involve physical devices, network-attached units, and even chip-based modules.
Able To Safe Your Enterprise?
A MAC is created by combining a secret key with the message via a cryptographic algorithm. The recipient, using the identical key, validates the MAC to verify the message is untampered and confirm the sender’s id. You can have a quantity of keys for a similar knowledge or the identical key for multiple recordsdata, key backup and recovery, and so forth.